With iOS 27, Apple introduces a native line of defense called Impersonation Risk Detection to tackle increasingly sophisticated social engineering scams.
From convincing fake text messages to callers posing as government agents or bank representatives, these attacks are notoriously difficult to block, as traditional phone security struggles when a victim is tricked into voluntarily initiating a payment or sharing account details.
Designed to detect potential fraud in real time, this new system-level feature in iOS 27 acts as a built-in safety net, warning you (and supporting third-party apps) if an interaction shows signs of a scam before handing over sensitive information or money.
Latest Videos FromTom the guide
How Apple Spots Scams Without Reading Your Private Messages
Unlike invasive security tools that scan your personal files, Identification risk detection is built around Apple’s privacy-first architecture.
If you attempt a sensitive action in a supported app—such as sending a wire transfer, making a high-value payment, or changing critical security settings—the app may request a risk assessment from iOS 27.
On the device, Apple analyzes interaction timing, behavioral patterns, context, and basic sensor data to determine if you are acting under the influence of a scammer.
Based on this on-device analysis, iOS 27 assigns one of three risk levels:
- Unknown: No actionable data or normal usage patterns detected.
- Medium: Small unusual activity marked.
- Height: Significant indicators of suspicious or manipulated behavior detected.
decisively, Apple never reads or analyzes the content of your photos, messages or mail.
The app only receives the final risk level score, which allows it to trigger protective measures such as requiring extra identity verification, delaying a transaction or displaying an urgent warning banner.
Why is the feature disabled by default?
Because Impersonation Risk Detection requires sharing limited event signals with app developers and system diagnostic servers, Apple leaves the feature disabled by default when updating to iOS 27.
To take advantage of the protection, you must manually opt-in through your settings.
How to enable impersonation risk detection in iOS 27
To set it up, open settings on your iPhone, scroll down, and tap on privacy and security.
Next, locate and select Impersonation Risk Detection, and then just turn on the main switch to grant consent for supported apps to request real-time risk assessments.
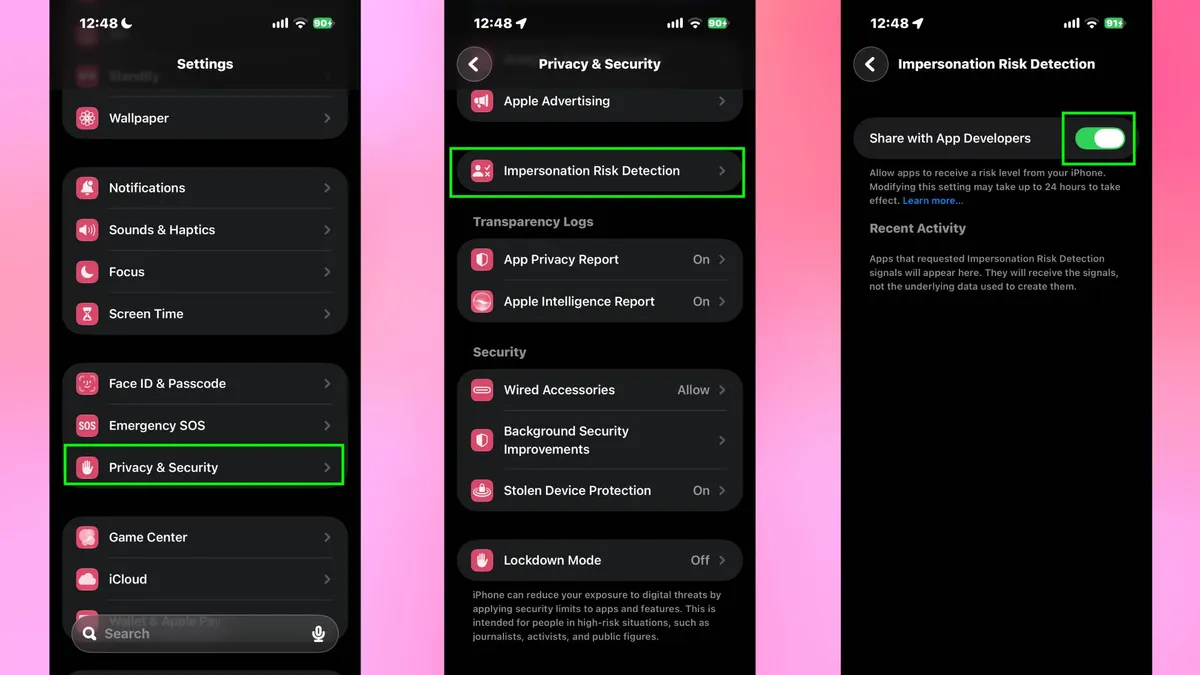
Apple notes that after enabling the toggle, it can take up to 24 hours for the protective signals to fully activate via compatible apps.
Once active, you can return to the same menu at any time to view Recent Activity, giving you full visibility into which apps have requested a risk assessment and the specific actions that triggered them.
Do you turn on impersonation risk detection, or would you rather turn off sharing? Let us know in the comments.
follow Tom’s Guide to Google News in the add us as a preferred source to get our latest news, analysis and reviews in your feeds. Make sure you click the follow button!